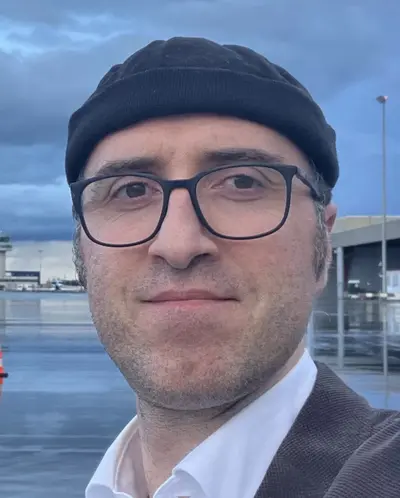
Germán Fuentes Capella
Engineer. Former CTO and CISO in European payments.
About me
My career has moved across engineering, CTO and CISO roles. That path is unusual and intentional: I think security and governance work better when they are built from within engineering, instead of decided from outside.
SDLC is where I see this go wrong most often. Well built, it supports velocity without sacrificing quality. In practice, it often means slow delivery, change committees, and engineering quality quietly degrading while the paperwork grows.
Today I work independently with payments companies, other regulated businesses, and technology companies newly in scope of regulation like DORA or CRA. Some hire me as an advisor; others bring me in as delivery lead, engineering lead, CTO or CISO.
How I work
Engineering first. Good delivery depends less on the code than on the work around it: clear requirements, automated tests, and metrics that show where things slow down. I still write code, in Java, Go and Python, because it keeps my judgment grounded in how the work actually gets done.
Governance built into engineering. Governance starts with what teams already do every day: standups, code reviews, vulnerability scans, deployments. I build the governance framework on those activities, in a form non-technical stakeholders understand and auditors accept. Governance always adds some overhead; the goal is to keep only what is necessary and adds value.
Automation where it pays. Automate a control once, maintain it like code, and evidence becomes a byproduct of the work instead of a project before every audit. The DORA RoI Health Check came out of that idea: thousands of automated checks, run in the browser before submission. Automation is not free: it needs owners and maintenance, so I start where manual effort or audit risk is highest.
Agents with boundaries. When an agent causes an incident, the agent is rarely the root cause. It is a probabilistic model that is very good at making changes, so it amplifies the weaknesses already there: loose user access, easy privilege escalation, thin monitoring. When it gets something wrong, nothing limits the damage or stops it. That is where I start: the basic controls, and a way to stop the agent. I build coderoom, an open-source shell for coding agents, around the same principle: loops with limits, checks that decide when the work is done, and the engineer in charge.
Selected work
Independent advisor (since October 2025)
Advisory, strategy and delivery for payments companies and other regulated businesses.
- Supported a DORA service provider’s entry into Germany: reviewed and corrected its Register of Information, aligned its structure with BaFin’s reporting requirements, and saw it through until its submissions passed BaFin’s technical validation.
- Built the DORA RoI Health Check, used by 15 institutions in the EU ahead of their regulatory submissions.
- Assessed CRA readiness for a vulnerability scanning vendor: a pipeline that automatically verifies the requirements its product already covers, and a roadmap for the gaps aligned with its product plans.
- Defined the architecture and delivery plan for the ground-up rebuild of a public-sector back-office platform.
PPRO (2020 to 2025)
Payments unicorn processing $9bn+ a year across 175+ markets, supervised by the CSSF and FCA. Director of Engineering, Interim CTO (2021) and Interim CISO (2024), as part of the executive leadership team.
- Led the DORA programme end to end, including the Register of Information; it passed internal audit without significant findings.
- As Interim CISO, led PCI DSS recertification and ISO 27001 activities.
- Led 200 engineers across 15 teams in EMEA, LATAM and APAC, and reorganised a flat structure into domain teams with clear ownership.
- Replaced centralised change committees with team-owned deployment, moving teams from weekly to daily deployments.
- Brought availability to 99.99% by shaping the data centre to AWS migration around reliability, and cut cloud costs by 40% (about €2m a year).
- Led the SWIFT MT to ISO 20022 migration and the Brexit-driven move of banking partners, both without service disruption.
ONPEX (2018 to 2020)
CSSF-supervised BaaS institution (about 20 people) providing cross-border collection and settlement for non-EU merchants. CTO.
- Hired to bring the payments platform to production; it went live within three months.
- Led the banking integrations, including SWIFT and ISO messaging, and built an architecture that handles failures at SWIFT, partner and internal levels.
PAY.ON and ACI Worldwide (until 2017)
Payment gateway serving merchants and PSPs, acquired by ACI Worldwide in 2015. Software engineer, then Head of Connector Development and Principal Product Manager.
- Managed a network of over 300 integrations with acquirers, card schemes, wallets and local payment methods.
- Led about 30 engineers across Germany, Serbia and Romania, and increased integration throughput fourfold.
- Owned product for payment orchestration: alternative and risk-based routing, failed-payment fallback and conversion monitoring.
Talks and tooling
I speak and write about applying engineering practices to audits, compliance and AI governance: LeadDev Berlin, GSDC, and the IIA Luxembourg and ISACA Luxembourg Chapter so far. Details and slides are on the Insights page.
Tools: the DORA RoI Health Check and coderoom.
I work in Spanish, English and German, from Valencia, with regular travel.
Looking for a delivery lead, an engineering lead, or an interim CTO or CISO?
Book a call to talk it through, or see how I can help.